CASE 04 / Side quests
Encrypting files without uploading them.
I rebuilt my internship encryption app around the browser's Web Crypto API, with password and recipient-key modes.
- THE PROJECT
- CipherDesk
- THE CONTEXT
- Avysh / Aavishk
- THE CHAPTER
- 2022 / Revisited
- THE PROBLEM
- Encrypt text and files without sending their contents to a server.
- WHAT I OWNED
- The browser-local rebuild, password and recipient-key workflows, and their interface.
- THE RESULT
- A hosted workspace using Web Crypto for AES-GCM encryption and RSA-wrapped content keys.
From the live product
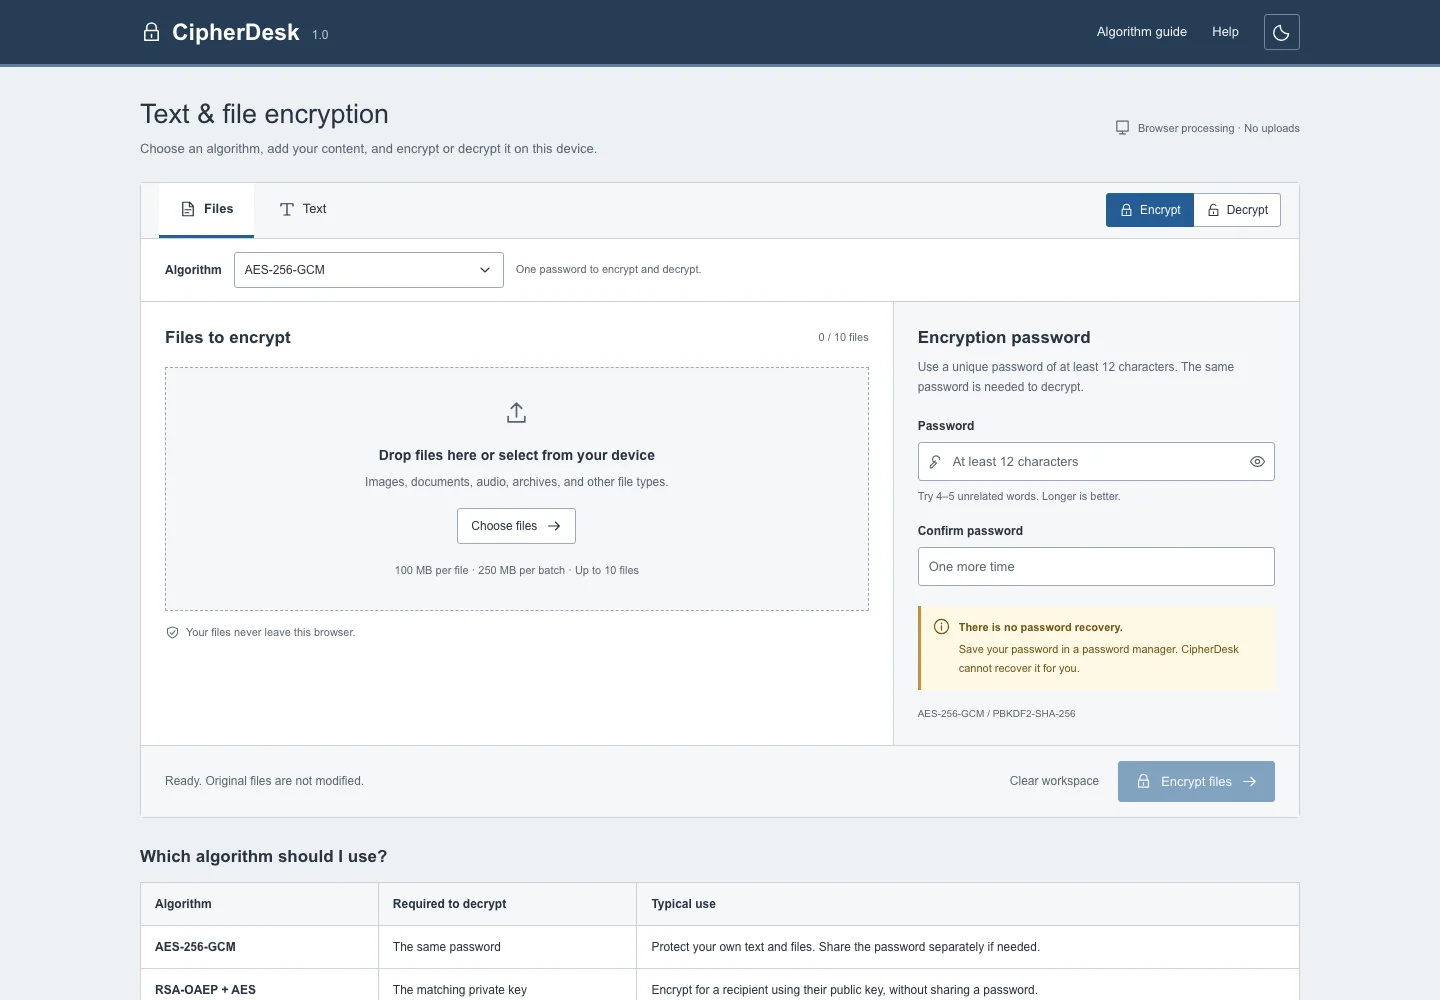
Public CipherDesk workspace, captured 28 October 2026. No files, passwords, or private keys were entered.
My contribution: The browser-local rebuild and its file, text, password, and recipient-key workflows. This screen shows the interface, not an independent security assessment.
01 / The problem.
My internship app processed encryption on a server. In CipherDesk, I moved text and file encryption into the browser, so the content does not need to be uploaded. The two workflows are different: share a password, or encrypt for someone whose public key you already have.
02 / My role.
This project began during my internship at Avysh (Aavishk Sustainable Solutions), where I developed an encryption/decryption web app with Node.js, Express, and EJS. CipherDesk is its current hosted evolution: browser-local text and file encryption using modern AES-GCM and hybrid RSA workflows, rather than the original server-side experiments with legacy algorithms.
- My contribution
- The original Avysh internship app and the later browser-local CipherDesk implementation.
- Shared scope
- Uses the browser's Web Crypto implementation. The linked repository contains the original internship app; the portfolio lab is a separate text-only demonstration, not a security audit.
- What changed
- A hosted text and file workspace with local processing, password encryption, and RSA-wrapped content keys.
03 / Implementation details.
- In recipient-key mode, generating a fresh AES key for the content and wrapping that key with RSA-OAEP.
- Rejecting a wrong key or altered encrypted file rather than returning unusable output.
- Warning before unsaved work is discarded and making key-import operations cancellable.
04 / The result.
- Text, images, and files are encrypted and decrypted on the device, without uploading the content or creating an account.
- RSA mode wraps a fresh AES key rather than trying to encrypt the whole file with RSA.
- The interface explains that a lost password or private key cannot be recovered by the app.